

Responsible AI Maturity Model: How to Assess Your Organization's Readiness
Readiness is not a feeling. It is something you can score, compare and improve. A responsible AI maturity model gives leaders a structured way to see where their organization stands today, what "good" looks like and which gaps matter most. Without one, programs tend to grow unevenly, with strong policy in one place and no testing in another. This guide explains how a maturity model works, what dimensions to assess and how to turn the results into a realistic plan. Professionals who want formal training in the field can explore the certified responsible AI expert certification.
What is a responsible AI maturity model?
A responsible AI maturity model is a framework that describes stages of capability in governing AI, from ad hoc and informal to managed and continually improving. Each stage sets out what practices, roles and evidence you would expect to see. You compare your current state against those descriptions to find your level and your gaps.

There is no single official model, and organizations often adapt one to their size, sector and risk. What matters is that the stages are clear, the criteria are observable and the assessment is repeated over time.
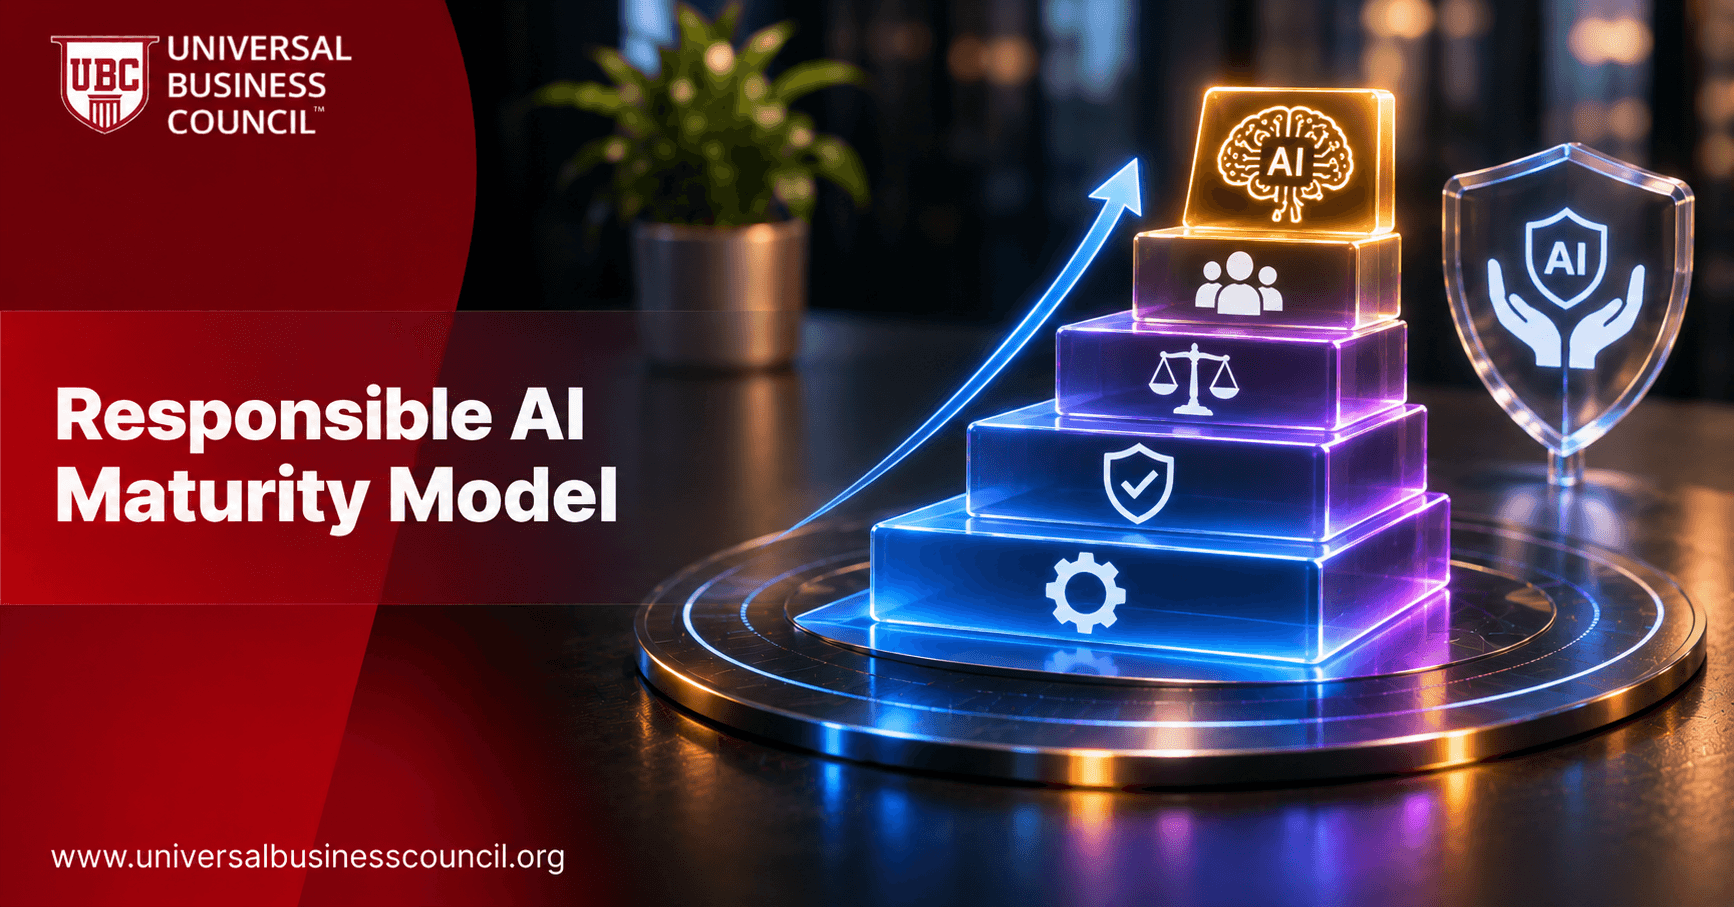
The typical maturity stages
Most models use four to five levels. The names vary, but the pattern is similar.
Initial: AI is used without shared rules, and responsibility is unclear
Developing: some policies and reviews exist, but they are inconsistent
Defined: standard processes, roles and documentation apply across the organization
Managed: performance is measured, monitored and reported to leadership
Optimizing: lessons feed back into the program, and practice adapts to new risks
Higher is not always better for every team. A small company using low-risk tools may be well served at the defined level. A bank or hospital deploying high-impact models needs to go further.
Dimensions to assess
Assess several dimensions separately, because maturity is rarely even.
Governance and accountability
Look for an executive sponsor, a review group, named owners for each system and clear decision rights. Ask whether leadership actually receives reports and acts on them.
Risk and compliance management
Check for an AI inventory, risk tiers, impact assessments for higher-risk uses and a process for tracking legal change. Mature programs link AI risk to enterprise risk management.
Data and model practices
Examine data quality, consent and provenance, testing for bias and robustness, documentation such as model cards and change control. These show whether principles reach the people who build and deploy systems.
Security and privacy integration
Responsible AI should connect to existing security and privacy programs. Check whether AI systems are covered by access controls, threat testing and data protection reviews.
People and culture
Assess training coverage, role clarity, willingness to raise concerns and whether teams feel review helps or slows them. Skills matter here, and many technical staff build foundations through tech certifications.
Monitoring and incident handling
Mature organizations monitor systems after launch, track agreed metrics, handle incidents through a defined process and record lessons learned.
How to run the assessment
A good assessment is evidence-based, not a self-congratulatory survey.
Collect evidence, not opinions
For each criterion, ask for proof: a policy, an approval record, a test report, a training log. Interview owners and sample real systems to confirm that practice matches paperwork.
Score consistently
Use a simple scale for each dimension and define what each score means. Have more than one assessor score independently, then reconcile differences. Keep the scoring sheet so you can repeat it later.
Involve different functions
Legal, privacy, security, data science, product, HR and business leaders all see different parts of the picture. Include them so that blind spots surface. Integrity of the evidence matters, and approaches to tamper-evident records connect to topics in deep tech certifications.
Turning results into a roadmap
Scores are useful only if they drive action.
Prioritize by risk
Close the gaps that expose you to the most harm first, such as missing human oversight on a high-impact system or no inventory of vendor AI. Cosmetic improvements can wait.
Set realistic targets
Aim for one level of improvement at a time in the dimensions that matter most. Assign owners, deadlines and measures of success for each action.
Build capability and verify it
Many gaps close with people, not tools. Train staff by role and confirm that those holding sensitive responsibilities have the qualifications they claim, with services like HireValid supporting credential checks.
Report honestly
Share progress with leadership, and be careful about external claims. Saying you have "mature" governance when the assessment shows gaps invites criticism. Communication teams can learn to describe progress accurately through a digital marketing course.
Common pitfalls
Organizations often over-score themselves, treat the assessment as a one-time project or collect so much detail that nothing is acted on. Others measure policy existence instead of policy use. Keep criteria observable, repeat the assessment on a schedule and tie results to named actions.
Conclusion
A responsible AI maturity model helps organizations assess readiness in a structured, repeatable way. Define clear stages, score governance, risk, data and model practice, people and monitoring using evidence, and involve several functions. Then prioritize gaps by risk, set realistic targets and report progress honestly. Reassess on a schedule, because readiness changes as your AI use and the rules around it change.
Frequently asked questions
These are the questions leaders ask most about maturity assessments.
1. What is a responsible AI maturity model?
A framework describing stages of capability in governing AI.
2. Is there one standard model?
No. Organizations adapt models to their size, sector and risk.
3. How many stages are typical?
Usually four to five, from initial to optimizing.
4. Why assess maturity?
To find gaps, set priorities and show progress.
5. What dimensions should we cover?
Governance, risk, data and models, security and privacy, people and monitoring.
6. Who should run the assessment?
A cross-functional group, ideally with independent scoring.
7. What counts as evidence?
Policies, approvals, test reports, training logs and system samples.
8. How do we avoid over-scoring?
Use observable criteria and have more than one assessor.
9. Should every organization aim for the top level?
No. Aim for a level that matches your risk.
10. How often should we reassess?
On a regular schedule, such as yearly, and after major changes.
11. What is the first gap to fix?
The one that exposes people or the business to the most harm.
12. How do we link it to enterprise risk?
Add AI risks to the existing register and reporting lines.
13. Can small companies use it?
Yes, with a lighter version.
14. Do maturity scores satisfy regulators?
No. They support planning but do not replace legal compliance.
15. What role does culture play?
A large one. People must feel able to raise concerns.
16. How does training affect maturity?
It raises practice quality and consistency across teams.
17. Should vendors be included?
Yes. Third-party AI is part of your risk.
18. How do we present results to leadership?
With simple scores, key gaps, owners and timelines.
19. Can we publish our maturity level?
Be cautious, and make sure claims match the evidence.
20. What is the biggest pitfall?
Treating the assessment as a one-time exercise with no follow-up.
Related Articles
View All
Artificial Intelligence
AI Model Cards Explained: Documentation for Responsible AI Systems
Learn what AI model cards are and how they support responsible AI development through clear and structured documentation. Explore the key information they contain, including model purpose, performance, limitations, intended use, risks, and evaluation results, and how they improve transparency and accountability.
Artificial Intelligence
Differential Privacy in AI: A Practical Guide for Organizations
Learn how differential privacy helps organizations protect sensitive information while developing and using AI systems. Explore how it works, key techniques, privacy budgets, practical applications, implementation challenges, and how businesses can use it to strengthen data protection and responsible AI practices.
Artificial Intelligence
Federated Learning and Responsible AI: Benefits, Risks and Limitations
Explore how federated learning supports responsible AI by allowing machine learning models to train across decentralized data sources without directly sharing raw data. Learn about its benefits for privacy and collaboration, along with risks, technical limitations, security concerns, and practical applications.
Trending Articles
The Role of Blockchain in Ethical AI Development
How blockchain technology is being used to promote transparency and accountability in artificial intelligence systems.
AWS Career Roadmap
A step-by-step guide to building a successful career in Amazon Web Services cloud computing.
Top 5 DeFi Platforms
Explore the leading decentralized finance platforms and what makes each one unique in the evolving DeFi landscape.