

Research & Knowledge Hub
1,550+ research articles, technical guides, and in-depth analyses authored by council members and industry experts.
Articles - Page 3
1,550 articles
Responsible AI in Banking and Finance: Fraud Detection, Credit Risk and Compliance
Explore how responsible AI is shaping banking and finance through fairer lending, smarter fraud detection, and more transparent financial services. Learn about key benefits, ethical risks, data privacy, regulatory challenges, and best practices for building trustworthy AI systems in finance.
Responsible AI in Healthcare: Safety, Privacy, Fairness and Accountability
Discover how responsible AI is transforming healthcare through safer, fairer, and more transparent applications. Explore its benefits, challenges, ethical considerations, and the importance of protecting patient data while improving clinical decision-making.
Human-in-the-Loop AI: Why Human Oversight Matters in Automated Decisions
Explore human-in-the-loop AI and why human oversight matters in automated decisions. Learn how human review helps reduce errors, address bias, improve accountability, and make AI systems safer and more reliable.
AI Guardrails Explained: How to Control Risks in Generative AI Applications
Learn what AI guardrails are and how they help control risks in generative AI applications. Explore key techniques for preventing harmful outputs, reducing bias, protecting sensitive data, and improving AI security while ensuring responsible and reliable AI deployment.
Deepfakes and Synthetic Media: Responsible AI Detection and Prevention
Understand what deepfakes and synthetic media are and explore how responsible AI can help detect and prevent their misuse. Learn about detection techniques, ethical challenges, digital authenticity, and practical strategies for reducing misinformation, protecting privacy, and promoting responsible AI use.
Responsible AI in RAG Systems: Data Privacy, Accuracy and Governance
Learn how to apply responsible AI principles to retrieval-augmented generation (RAG) systems. Explore key considerations for protecting data privacy, improving response accuracy, reducing bias, and establishing effective governance to build secure, transparent, and trustworthy RAG applications.
OpenAI Dots Pricing and Usage Limits: Guide for Business Teams
Explore OpenAI Dots pricing and usage limits for business teams. Learn how subscription costs, usage allowances, and plan features affect budgeting, resource allocation, and the practical use of AI agents in business workflows.
AI Red Teaming Explained: Testing Generative AI for Safety and Security
Learn what AI red teaming is and how it helps test generative AI systems for safety, security, and reliability. Explore common testing methods, potential vulnerabilities, prompt injection risks, and best practices for identifying weaknesses and improving AI safeguards.
Responsible AI for AI Agents: Autonomy, Control and Human Oversight
Explore how responsible AI principles apply to autonomous AI agents and understand the importance of autonomy, control, and human oversight. Learn how organizations can manage agentic AI risks, establish safeguards, maintain accountability, and ensure AI agents operate safely, transparently, and within defined boundaries.
Responsible Prompt Engineering: Privacy, Bias and Security Best Practices
Learn how to practice responsible prompt engineering while protecting privacy, reducing bias, and maintaining AI security. Explore best practices for writing safe and effective prompts, handling sensitive information, preventing harmful outputs, and using generative AI responsibly across personal and business applications.
AI Hallucinations: Causes, Risks and Responsible Mitigation Strategies
Understand what AI hallucinations are, why they occur, and the risks they pose to individuals and organizations. Explore common causes, real-world implications, and responsible mitigation strategies, including human oversight, reliable data sources, model evaluation, and continuous monitoring to improve AI accuracy and trustworthiness.
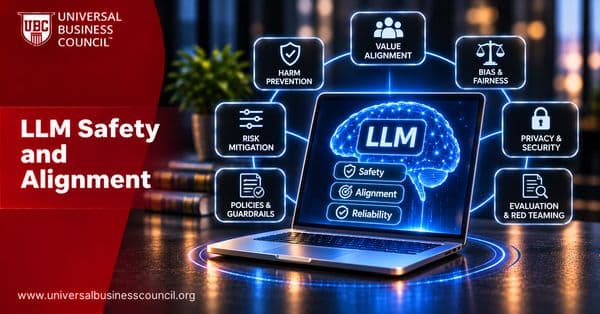
LLM Safety and Alignment: How to Build More Reliable AI Systems
Explore LLM safety and alignment and understand how developers can build more reliable AI systems. Learn about key techniques for reducing harmful outputs, improving model behavior, preventing misuse, addressing bias, and aligning large language models with human values and expectations.